
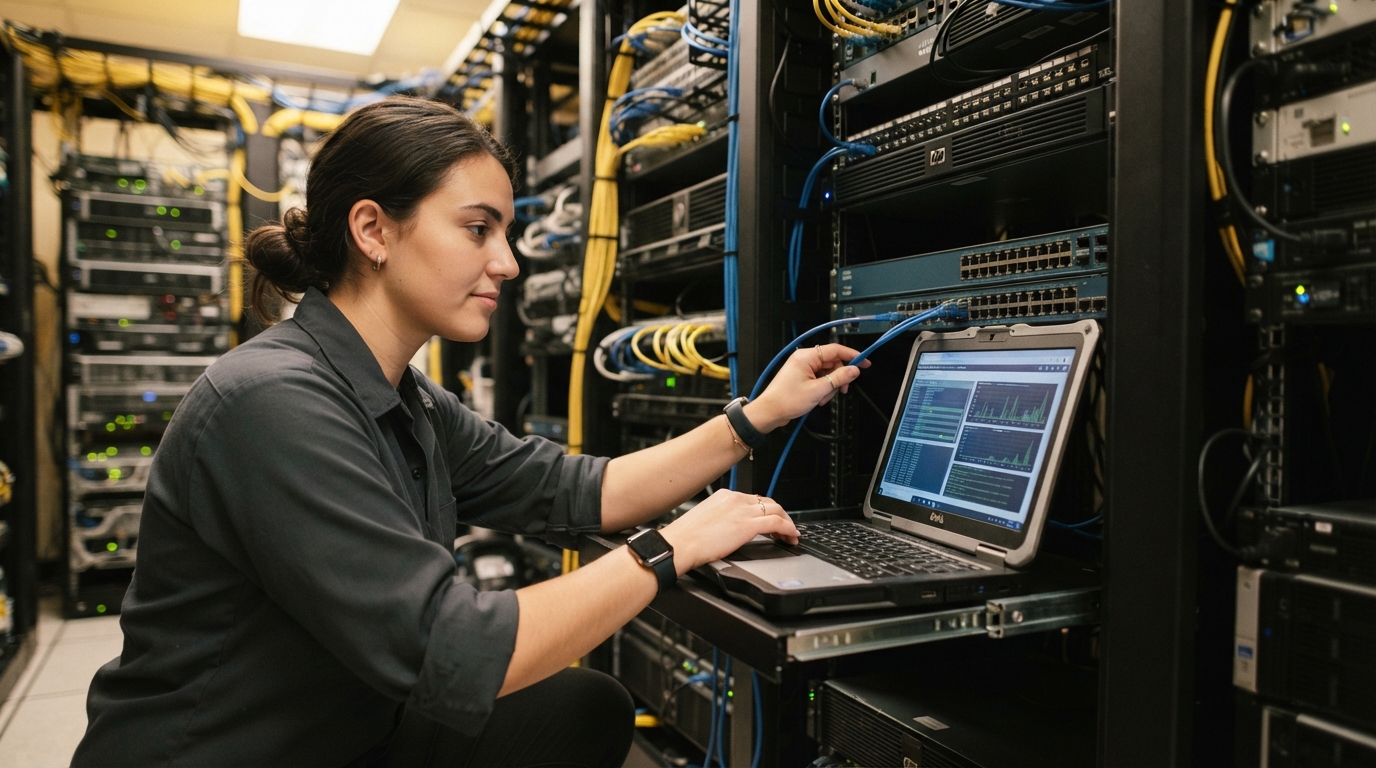
- Managed IT services combine continuous monitoring, patching, and helpdesk support to reduce downtime and close common security gaps.
- Denver, CO businesses increasingly rely on outside IT providers for predictable monthly costs instead of reactive, break-fix repairs.
- Phishing remains the top entry point for cyberattacks, making proactive monitoring and employee training a core part of any managed IT plan.
Businesses searching for stable, affordable technology support often land on the same conclusion: outsourcing day-to-day IT management reduces downtime and strengthens defenses more reliably than handling it internally. Managed IT Services Denver CO typically bundle monitoring, patching, helpdesk access, and security oversight into one predictable arrangement, which is why the model has become a common choice for small and mid-sized companies that lack a full internal IT department.
For many organizations, the appeal is less about adding technology and more about removing uncertainty. A provider that watches systems around the clock can catch failing hardware, unpatched software, or suspicious login activity before it turns into a full outage or breach.
What Managed IT Services Typically Include
Most managed IT arrangements are structured around a few recurring functions rather than one-off repairs. These generally include:
• Continuous network and system monitoring to flag irregular activity
• Automated patch management so software vulnerabilities get closed quickly
• Helpdesk support for day-to-day employee technology issues
• Server and network administration
• Strategic IT consulting tied to business goals rather than just troubleshooting
This structure shifts IT from a reactive cost center into a planned, ongoing function with a predictable monthly fee rather than unpredictable repair bills.
Why Security Depends on Proactive Monitoring
Security is rarely about a single tool. It depends on consistent attention to patching, access control, and employee behavior over time. According to CISA’s cybersecurity guidance for businesses, core practices such as phishing awareness training, strong password requirements, multifactor authentication, and regular software updates form the baseline for reducing risk.
Phishing deserves particular attention. Industry research cited in a 2025 small business cybersecurity guide found that more than 90% of successful cyberattacks begin with a phishing email, which underscores why ongoing employee training matters as much as technical controls. A managed IT provider that folds phishing simulations and awareness training into its service helps close that gap without requiring a business to build an internal security program from scratch.
CISA also recommends that organizations of any size maintain a basic incident response plan, covering who to contact and how to contain damage if something does go wrong. That kind of planning is typically easier to execute consistently when a provider already monitors the environment day to day, rather than being assembled after an incident occurs.
Efficiency Gains Beyond Security
Security is one half of the value proposition; operational efficiency is the other. Predictable monthly IT costs let businesses budget technology spending the way they budget rent or payroll, instead of absorbing surprise repair invoices.
|
Approach |
Cost Pattern |
Typical Response |
|
Break-fix IT support |
Unpredictable, billed per incident |
Reactive, after failure occurs |
|
Internal IT hire |
Fixed salary, limited coverage hours |
Reactive and proactive, but limited by staff size |
|
Managed IT services |
Flat monthly fee |
Proactive monitoring with faster issue detection |
Denver’s business environment includes a mix of established firms and growing small companies, many of which operate with lean internal staff. For these organizations, continuous monitoring and helpdesk access reduce the time employees spend working around technology problems instead of through them.
Choosing a Managed IT Approach
Businesses evaluating providers generally look for a few concrete signals rather than marketing claims:
1. Clear documentation of what is monitored and how often
2. A defined patching and update schedule
3. Transparent, flat-rate pricing without hidden tiers
4. Evidence of security practices aligned with recognized frameworks, such as those referenced by CISA and NIST
Based in USA, technology providers serving the Denver, CO market apply these same fundamentals, adapting scope and support hours to each client’s operational needs. Published information for Rocky Mountain Tech Team outlines its managed IT offerings for businesses operating in that service area.
Frequently Asked Questions
What is the difference between managed IT services and traditional IT support? Traditional support typically responds after something breaks, while managed services apply continuous monitoring and maintenance intended to prevent issues before they disrupt operations.
Do managed IT services replace an internal IT staff member? Not necessarily. Many businesses use managed services alongside an internal hire, with the provider adding monitoring capacity, specialized security knowledge, or after-hours coverage.
How does phishing training fit into managed IT services? Because phishing causes the large majority of successful attacks, ongoing employee training and simulated phishing tests are commonly included in managed security offerings rather than treated as a separate project.
Is a flat monthly fee standard across providers? Pricing structures vary, but flat-rate monthly billing is a common model because it lets businesses forecast technology costs without per-incident surprises.
Next Steps for Evaluating IT Support
Business owners weighing managed IT options can review service documentation before making budget decisions. Current details for Rocky Mountain Tech Team are published online for businesses comparing monitoring, patching, and support options in the region.